WordPressWordPress es el software de blogs líder en el mundo, y es concretamente fácil de utilizar y adaptable. Con WordPress, es factible crear con éxito sitios web con la ayuda de funciones ya predefinidas, sin mucho esfuerzo, y para proporcionar contenido como texto, imagen y vídeo. No se requiere conocimiento de HTML. WordPress además facilita la gestión y el mantenimiento de contenidos extensos. Al mismo tiempo de su fácil manejo, plus es uno de los sistemas de gestión de contentsEl contenido puede ser muy difícil de definir con precisión. Es una definición que se refiere a las declaraciones contenidas en un documento o publicación de cualquier tipo y puede incluir las tecnologías de la información y la comunicación. Esto cubre todos los tipos de medios como imágenes y texto. A parte de esto, en el campo de la optimización de motores de búsqueda, los términos duplicar contenido, contenido único, plus más conocidos y populares del mundo. Por consiguiente, WordPress es un target¿Qué es un objetivo?En marketing, un objetivo es el resultado que se pretende alcanzar en un periodo de tiempo, a través el uso de los recursos disponibles. Por tanto, se debe formular de una forma clara y hace falta que sea accesible y medible. plus usual de vulnerabilidades de seguridad, como ataques de fuerza bruta, inyección SQL, malwareEl malware (compuesto por las palabras malicia y software) es un programa que ha sido desarrollado para realizar funciones indeseables que generan daño al usuario. Al principio, el objetivo del malware era irritar a los individuos, pero esto se ha expandido rápidamente hacia el espionaje sistemático y el robo de información personal. Las víctimas ya no son sólo individuos, sino además grandes instituciones como los bancos. El alcance del uso plus, secuencias de comandos entre sitios y ataques DDoS. De hecho, recientemente, una nueva variedad de malware llamada Clipsa is launching brute force attacks on WordPress sites, stealing cryptocurrencies by hijacking the clipboard.
WordPress is only as secure as the amount of effort you put into improving the security of your site. As a website owner, it is your responsibility to stay alert and implement a proactive security strategy to prevent malicious attacks. The use of weak passwords and usernames, the failure to update the core and WordPress plugins, and poor quality hosting are among the common security mistakes that website owners make, making it easy for hackers to access. Malicious computer scientists.
WordPress es un CMSConcepto de CMS¿Qué es un CMS o Sistema de Administración de Contenido?Un CMS, siglas de Content Management System, es un tipo de software que se elabora con la finalidad de ofrecer una plataforma con la que facilitar la gestión y la administración de contenidos de cualquier web. Son herramientas pensadas para que cualquier persona, sin tener conocimiento alguno de informática, pueda publicar contenidos en una página sin ningún tipo de plus altamente seguro a su manera. A pesar de todo, mantener su sitio con WordPress a salvo de los ciberdelincuentes requiere que mejore su postura de seguridad y su credibilidad en línea. Pasos simples como actualizar el núcleo de WordPress, elegir un proveedor de alojamiento de WordPress seguro, prestar atención a domain name Security and the use of a strong password can help block malicious bots and attackers.
In this post, we will focus on WordPress salts and security keys and their role in ensuring that you don't have to deal with the consequences of malware attacks.
What are WordPress security keys and salts?
When a user logs into the WordPress site, various cookies are created on the computer. These are used to verify the identity of registered users. If a hacker enters your database or finds your cookies, they may be able to read your password, making your site vulnerable to attack.
WordPress usa claves de seguridad y sales para brindarle una salida críptica que se almacena en la base de datos o en la cookieUna cookie es un registro que es almacenado por un servidor web en el disco duro del usuario. El archivo recibido es una combinación de caracteres formada por números y letras, que asigna una cierta identidad al usuario (cliente). No podrán exceder un tamaño máximo de 4 KB y contendrán, por ejemplo, información sobre la extensión de la visita o sobre lo que el usuario haya pulsado. Cuando el cliente plus, lo que agrega una capa de seguridad a su sitio web.
Two of these cookies are:
- WordPress_ [hash] It is used only in the admin page or in the WordPress dashboard.
- WordPress_logged_in_ [hash] used in WordPress to determine if you are logged into WordPress.
The authentication details stored in these cookies by WordPress are hashed (cryptic values assigned) using the random patterns that are specified in the WordPress security keys.
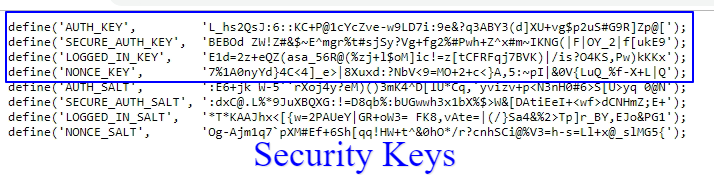
WordPress security key is a password that contains a set of long, complicated, random variables that enhance encryption, making it almost impossible to crack your password. The latest version of WordPress uses four security keys, each with its corresponding salt that can increase the security of your WordPress website.
These are:
- AUTHENTICATION KEY se puede utilizar para realizar cambios en el sitio. Le ayuda a firmar la cookie de autorización para no SSLLa encriptación SSL (Secure Socket Layer) proporciona una conexión segura entre el cliente y el servidor. Consiste en un protocolo de Internet que permite encriptar datos sensibles (como información de pago, datos de tarjetas de crédito) y hacerlos ilegibles a terceros. Al mismo tiempo, un certificado confirma que el servidor es fiable. En este momento, además se le llama TLS (Transport Layer Security). Relevancia SSL es un método de cifrado plus.
- SECURE_AUTH_KEY It is used to sign the authorization cookie for the SSL administrator and is used to make changes to the website.
- LOGGED_IN_KEY It is used to create a cookie for a user who is logged in. It cannot be used to make changes to the site.
- NONCE_KEY is used to sign the nonce key. This key protects the nonces from being generated, thus protecting your site from attacks.
You will find these keys and authentication salts in the wp-config.php file, located in the WordPress root folder.
WordPress sales they are random data strings that encode the security keys and add an additional layer of protection to the site and your credentials.
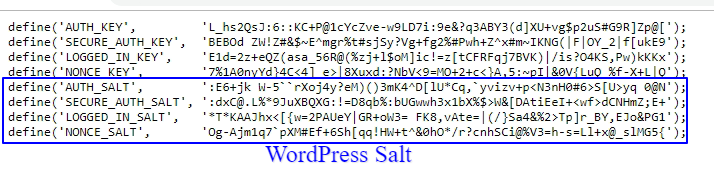
As you can see in this image, each security key has a corresponding salt, namely AUTH_SALT, SECURE_AUTH_SALT, LOGGED_IN_SALT, and NONCE_SALT.
Why use WordPress security keys and sales?
WordPress uses cookies to track the identity of users who log into its website. These cookies are stored in your site's control panel account, in other words, on the client side. For better encryption, authentication details (both username and password) are encrypted using a set of random values specified in WordPress security keys.
Thus, a randomly generated encrypted password such as "65a3ds2873ba27us36sd89s0fc" is extremely difficult to crack compared to an unencrypted one. Thus, website owners must use WordPress security keys to protect their site's cookies and prevent malicious hackers from accessing the site.
How to change WordPRess keys and salts manually
You can configure secret keys and salts manually or through a WordPress security plugin. If you have a self-hosted WordPress site, you will have to add the security keys yourself.
Please note: we only recommend manually editing WordPress files if you are a developer or comfortable working with code at an intermediate level or higher. If you are a beginner, skip to the recommended plugins below.
First, use the random generator in WordPress to get a unique secret key.
A continuación, inicie sesión en el administrador de archivos de su panel de control o a través FTPConcepto de FTP/¿Qué es el FTP?Un FTP, siglas de Protocolo de Transferencia de Archivos (File Transfer Protocol), es un sistema que se emplea para transferir datos entre un PC local y la web, o viceversa, que suele encontrarse siempre disponible dentro del alojamiento de cualquier compañía que haya contratado los servicios de uno para alojar un dominio y llevar adelante todas esas tareas imprescindibles para abrir una página web. Es plus. Desde aquí ubique el archivo wp-config.php para modificarlo.
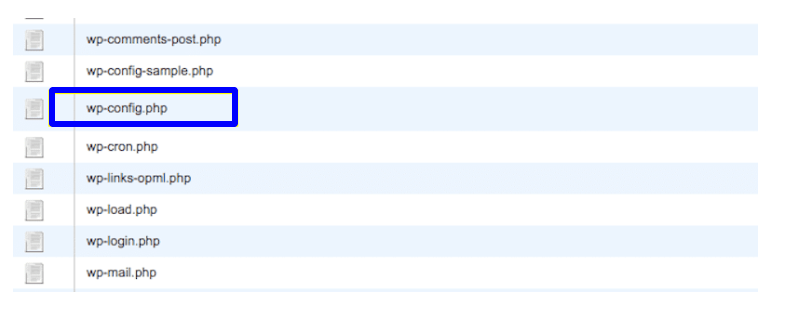
Open the file and scroll down to the "Authentication keys and unique salts" section. This is where you can add the secret keys that you previously generated.
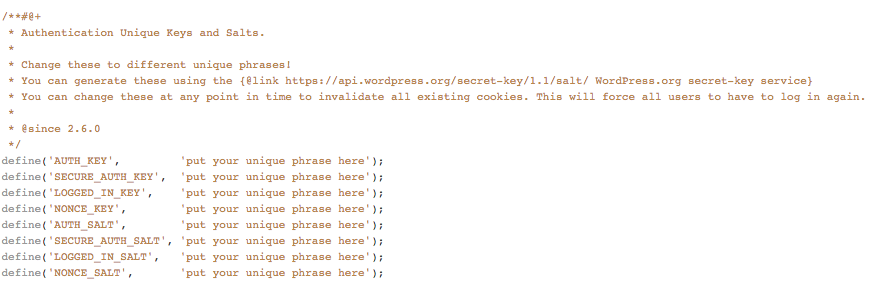
Once you save the file, you will be prompted to log in again.
Use a plugin to update keys and sales
Like most things in WordPress, you don't have to do it manually. Various WordPress plugins can be used to automate the process on your behalf. They are a quick and easy way to change your passwords and exit WordPress. Here are two that we recommend.
IThemes Security
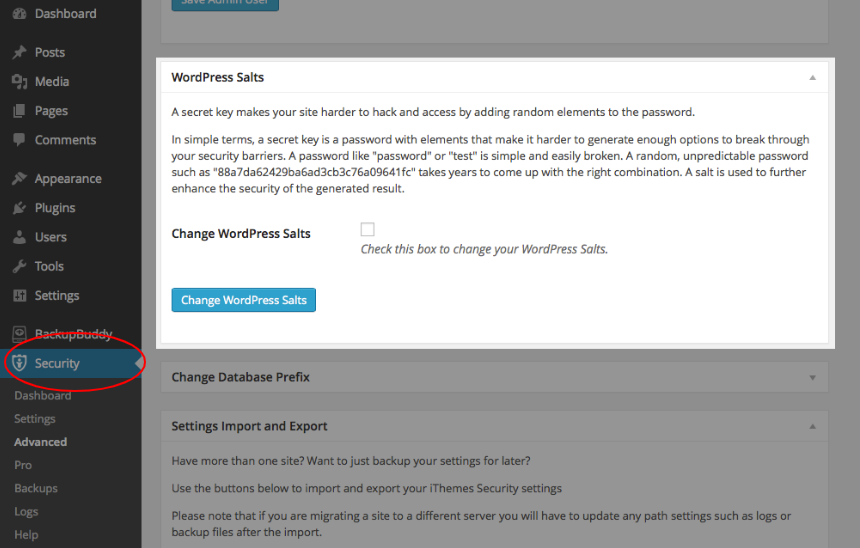
The current version of iThemes Security (Free v4.6 + or iThemes Security Pro v1.14 +) comes with a time-saving security feature that easily updates WordPress security keys and exits. It offers an update reminder every month and avoids the need to manually generate a new set of keys or edit your wp-config.php file.
To update the keys and sales, go to the 'WordPress Sales' section in the 'Advanced' tab, click on the checkbox next to 'Change WordPress sales' and in conclusion click on the 'Change sales' button WordPress'.
IThemes Security Pro ofrece funciones adicionales como autenticación de dos factores, escaneo programado de malware y reCAPTCHA para detectar softwareConcepto de Software¿Qué es el Software y cuál es su función?Un Software es la parte lógica, o más bien el soporte lógico, de cualquier sistema de tipo informático. Sea un PC, un teléfono teléfono celular o inclusive una tablet, es todo aquel programa que se ejecuta en él gracias a la coordinación de la parte física, es decir, el hardware, para llevar adelante alguna tarea concretamente o un recopilatorio de plus malicioso y agregar una capa adicional de seguridad a sus páginas de inicio de sesión de WordPress.
Salt shaker
Similarly, Salt Shaker offers impressive features and settings like manual and immediate WP security keys and sales changes to enhance WordPress security.
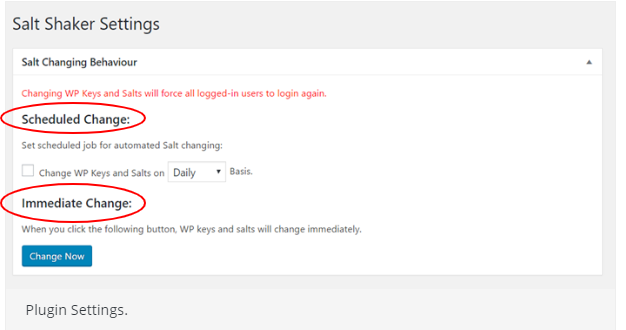
At the same time, after installing the Salt Shaker plugin, you can configure the scheduled job for automatic salt change. All you need to do is check the box and choose daily, weekly or monthly settings.
In both cases, the plugin is programmed to send automatic reminders to update WordPress keys. As a consequence, it simultaneously forces all registered users to go through the login process again. All of these features help protect a website from brute force attacks and other hacking attempts.
When it comes to protecting your WordPress site, prevention is the way to proceed. The strong combination of security keys and WordPress exits makes it difficult for hackers to crack website passwords. This is how WordPress offers improved security for user sessions and protects data.
Finally, here are some things to keep in mind when updating security keys and WordPress exits.
- After starting your WordPress site, change the security keys and the salts.
- Always use the WordPress salt key generator to create security keys. Do not do it yourself. Alternatively, you can automate the process using a WordPress plugin.
- Updating the security keys and WordPress exits will invalidate all existing cookies, causing all users to be disconnected instantly. So, when changing them, keep in mind that some users may be online.
- If you see signs that your site is under attack, update WordPress security keys and encourage your users to change their password.
Have a question about security keys and salts? Or tips that you would add? Let us know in the comments!